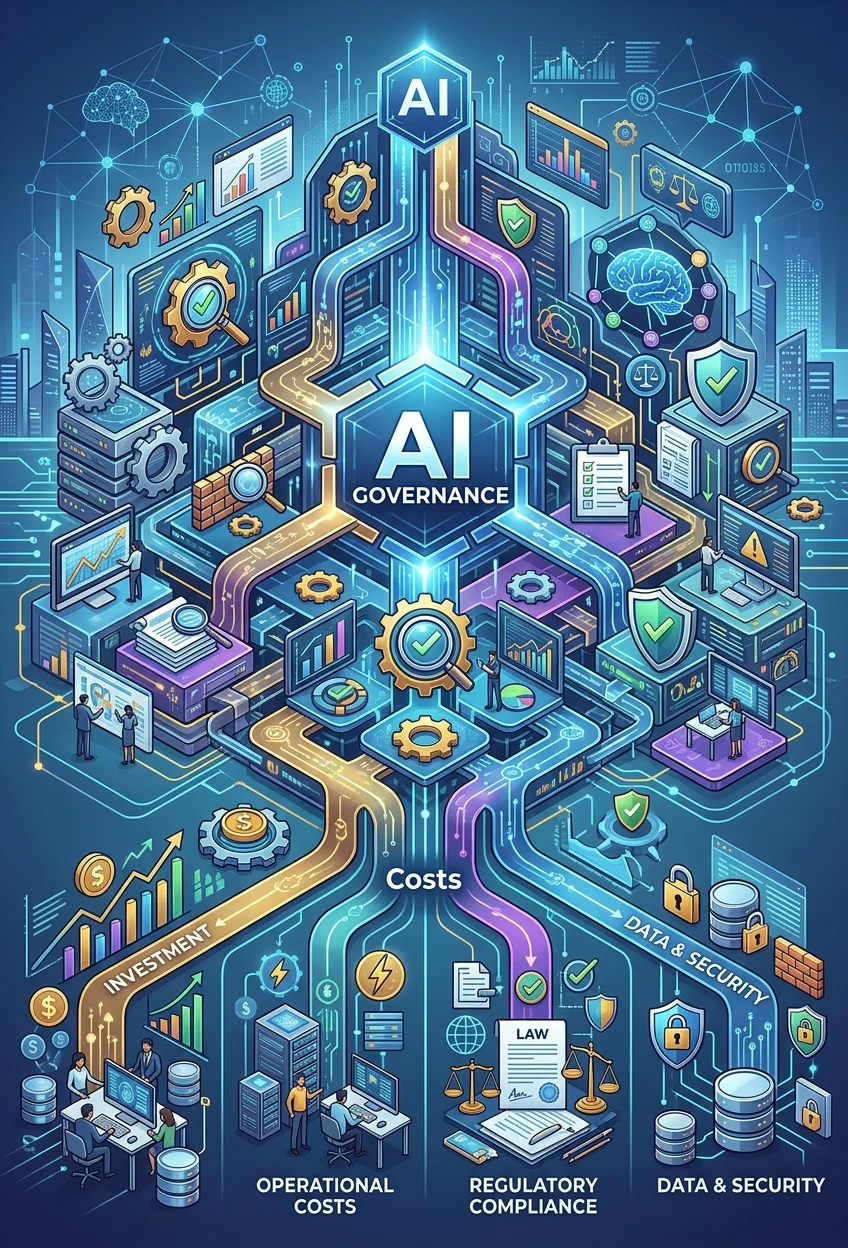
An AI tool making decisions your organization can’t explain, defend, or document is no longer just a technical loose end – under Oman’s current AI Policy and data protection law, it’s a compliance exposure. Through Falcon Pro AI, our enterprise AI platform, Lyqa Tech Ventures SPC helps businesses across Oman assess, document, and govern the AI systems they already use, so leadership can deploy AI with a defensible framework behind it instead of a policy gap waiting to be found.
We’re an Omani-owned technology company working across Muscat, Sohar, Salalah and Duqm. Falcon Pro AI is our own enterprise AI product, not a resold or partnered platform – so the same team that scopes your AI risk also builds the framework, writes the documentation, and stays on to review it as your AI use and Oman’s regulatory landscape both move forward.
A number of providers still frame AI governance in Oman as best-practice advice rather than a live regulatory expectation. That framing is behind the times, and it matters if you're preparing documentation for a client, auditor, or government tender.
The Ministry of Transport, Communications and Information Technology (MTCIT) issued the Public Policy for the Safe and Ethical Use of Artificial Intelligence in April 2025, built around accountability, transparency, human-centricity and social responsibility, and applied across the AI system's full lifecycle rather than just at launch. It sits inside the broader National Programme for Artificial Intelligence and Advanced Digital Technologies (2024–2026), and Oman opened its first AI Special Economic Zone in Muscat under Royal Decree 50/2026, signalling that AI oversight in the Sultanate is moving from framework to active implementation.
What your organization needs to have in place depends on what the AI system does and what data it touches - a customer-facing chatbot, a credit-scoring model and an HR screening tool are not governed identically.
Two consequences follow that catch organizations off guard:
Approval and documentation come before deployment, not after. Public-sector AI procurement in Oman already requires a formal pre-deployment risk assessment and sign-off before a system can be used or supplied.
Personal data doesn't get a separate exemption. If an AI system processes customer, patient, or employee data, it also has to satisfy Oman's Personal Data Protection Law (Royal Decree 6/2022) and its Executive Regulations - consent, data minimization and data-subject rights apply whether a person or a model is doing the processing.
In our experience, the gap is rarely the AI tool itself. It's the absence of a paper trail behind it: no documented risk assessment before adoption, no named person accountable for an AI-driven decision, no record of what data the tool was allowed to see, and no plan for explaining an automated outcome if a customer or regulator asks.
We map every AI tool already in use across your organization - including tools staff adopted on their own - and score each one against MTCIT's AI Policy principles and PDPL exposure, so you know where the real risk sits before you build anything.
We design the approval workflow, accountability structure and policy set your organization actually needs, sized to how much AI you run today - not a framework built for a scale of AI use you don't have.
Written AI use policies, a risk register, and the pre-deployment assessment documentation that public-sector procurement and larger private clients increasingly expect to see.
Confirming every AI system that touches personal data has a lawful basis under Oman's PDPL, with consent and data minimization built into how the system is used, not bolted on afterward.
Practical, role-specific training so staff know what they can put into an AI tool, what they can't, and who to escalate a concern to - the policy only works if the people using AI daily understand it.
A scheduled review cycle that keeps your framework current as your AI use expands and as Oman's AI regulation moves from framework into enforcement.
Not every AI deployment carries the same weight:
Credit scoring, fraud detection and other financial-decision models, where a wrong or unexplainable output has direct regulatory and customer consequences.
Diagnostic support, patient triage or records-handling AI in healthcare settings, where patient data protection and clinical accountability both apply.
HR screening and recruitment AI, where bias and explainability directly affect candidates' rights.
AI used in government-facing bids and public-sector service delivery, where pre-deployment approval is already a procurement requirement.
Customer-facing AI (chatbots, recommendation engines, dynamic pricing) that processes personal data at scale.
A direct comparison to show what changes when AI adoption has a governance framework behind it.
|
☷
Factor
|
▣
Ad Hoc AI Use
|
⌘
Governed AI Use
|
|---|---|---|
|
●
Accountability
|
No named owner for AI-driven decisions | Clear accountability assigned per system |
|
↗
Deployment
|
Tools adopted informally, department by department | Reviewed and approved before deployment |
|
$
Regulatory Exposure
|
Unknown until an audit or complaint surfaces it | Documented and monitored on an ongoing basis |
|
⇄
Data Handling
|
Personal data flows into tools without a checked legal basis | PDPL basis confirmed before data reaches the system |
|
◉
Explainability
|
No process for explaining an automated outcome | Documented rationale available on request |
|
+
Procurement Readiness
|
Bids stall without pre-deployment approval evidence | Documentation ready for public-sector submission |
|
⚙
Long-Term Cost
|
Reactive fixes once a gap is found | Predictable review cycle, fewer surprises |
|
⚙
Confidence to Scale
|
Growth outpaces oversight | Framework scales with AI adoption |
Banks and financial services AI governance
We identify every AI system in active or planned use across your organization, including tools adopted outside IT's visibility.
Each use case is scored against MTCIT's AI Policy principles and PDPL exposure to establish where the real risk sits.
policies, approval workflow, risk register and accountability structure built to match your actual AI footprint.
We help roll the framework out with the teams actually using AI day to day, not just hand over a document.
scheduled check-ins keep the framework current as your AI use grows and as Oman's AI regulation matures.
Scheduled review and refinement as your data, systems and business needs change.
Tell us which AI tools your organization is currently using or planning to adopt, and we'll tell you what governance you actually need before we scope anything.
Lyqa Tech don't publish fixed prices, because the real number depends on your AI footprint. These are the variables that actually move it:
Number and complexity of AI systems in use or planned across the organization.
Whether personal or sensitive data is involved, and how much of it.
Whether you're a public-sector supplier requiring formal pre-deployment approval documentation.
Sector-specific regulatory obligations - financial services and healthcare carry more than a general retail or hospitality use case.
Depth of staff training and change management required across departments.
Whether you need a one-time framework build or an ongoing monitoring and review engagement.
Financial services and Central Bank oversight
Healthcare data sensitivity and clinical accountability
Public sector procurement and pre-deployment approval
Local Infrastructure Planning
Omani-owned, Muscat-based - with the local standing that matters when you're preparing documentation for a government tender or public-sector client.
Delivered through Falcon Pro AI, our own enterprise AI platform - governance is built by the same team that owns the product, not outsourced to a separate compliance vendor guessing at how the system actually works.
Built on an existing security and data protection foundation - our AI governance work sits alongside the cybersecurity and IT infrastructure services we already deliver, not as a bolted-on compliance product.
Frameworks scoped to your actual AI use, not a generic template sized for a business much larger or smaller than yours.
One accountable team from the initial risk assessment through to ongoing review, so responsibility for your governance framework doesn't sit with three different vendors.
Tell us which AI tools your organization is currently using or planning to adopt, and we'll tell you what governance you actually need before we scope anything.
It’s active regulation, not just guidance. MTCIT’s Public Policy for the Safe and Ethical Use of AI (April 2025) sets a risk-based governance framework, and public-sector AI procurement already requires pre-deployment approval. Oman’s Personal Data Protection Law applies on top of that wherever an AI system processes personal data.
Falcon Pro AI is our enterprise AI platform first – governance and compliance services are delivered on top of it and alongside any other AI tools your organization already uses, so you’re not limited to only governing what we’ve built for you.
Yes. The obligation is about how AI is used and what data it touches, not whether you built the underlying model. A third-party chatbot or analytics tool that processes customer data still needs to sit inside a governance framework.
It depends on how many AI systems are in use and how sensitive the data involved is. A framework covering a handful of use cases can often be scoped and delivered in a few weeks; broader, multi-department engagements take longer.
It overlaps significantly. Any AI system handling personal data needs to satisfy the PDPL as well as MTCIT’s AI Policy, and we handle both together rather than as two separate compliance projects.