Threat Detection and Response Services in Oman

Had a close call you only found out about after the fact, or worried that an intrusion could sit in your network for weeks before anyone notices? Lyqa Tech Ventures designs, deploys and operates continuous threat detection and response programs for organizations across Oman – from a single-office SME in Muscat to a multi-site operation spanning an industrial free zone.

We are an Omani-owned technology company registered as an SME, working across Muscat, Sohar, Salalah and Duqm. You get one team accountable for the monitoring architecture, the detection tuning, the incident response, and the reporting that keeps your security posture – and your compliance record – current.

When structured threat monitoring becomes necessary in Oman

The bodies shaping Oman's cybersecurity expectations

Oman's cybersecurity landscape is coordinated by more than one authority, and knowing who oversees what matters when you're deciding how much monitoring your organization actually needs. The Oman National CERT (OCERT), operating since 2010, acts as the national focal point for incident response, threat advisories and coordination between public and private entities. National Cyber Governance and Assurance Affairs sets standards, accredits cybersecurity service providers, and issues assurance certification for systems and devices. A dedicated Cyber Defense Centre, established by royal decree, carries a broader national cyber-defense mandate. Sector regulators layer on top of this: the Telecommunications Regulatory Authority for telecom and ISP operators, and the Central Bank of Oman for licensed financial institutions.

The bodies shaping Oman's cybersecurity expectations

The obligations that typically apply to your organization

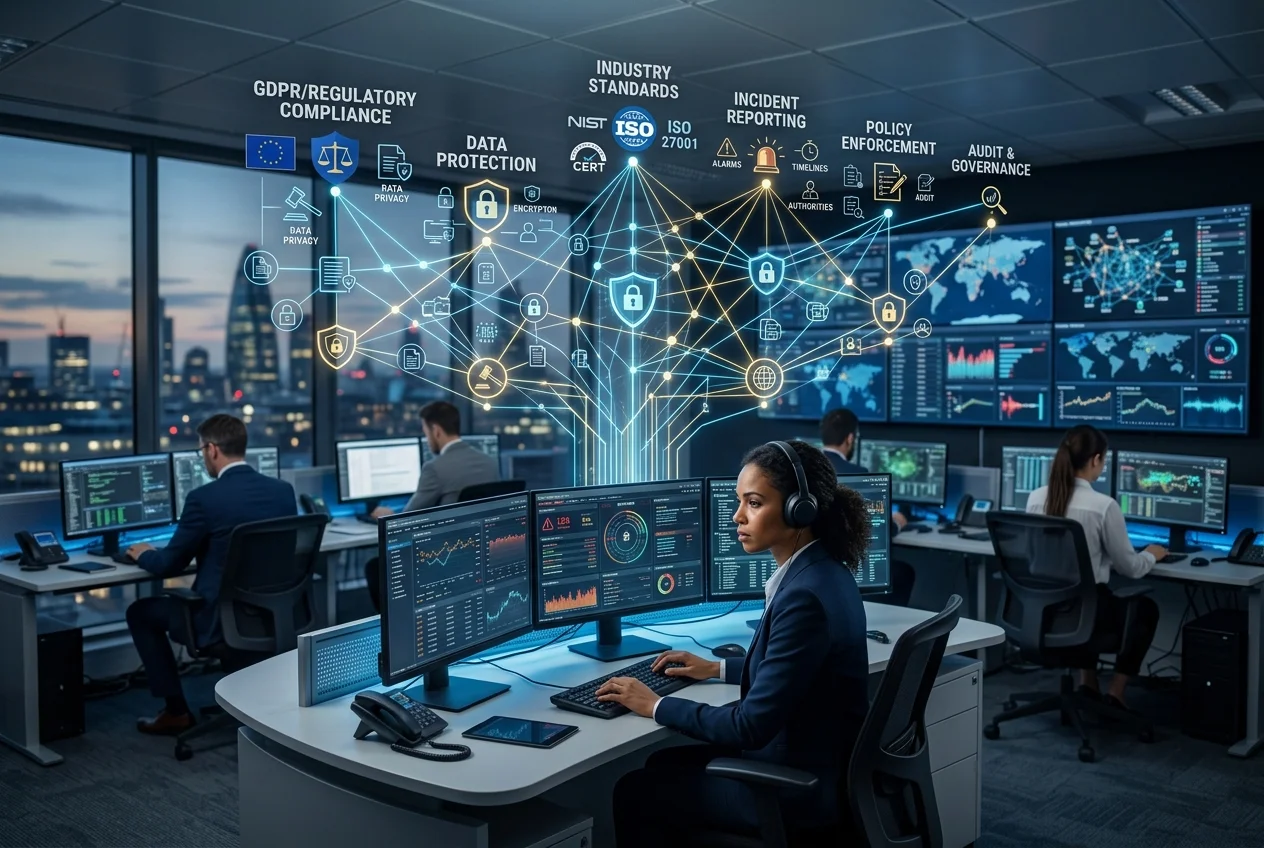
Your obligations depend on your sector and the data you hold, not just your size. Oman's Personal Data Protection Law covers how personal data is collected, processed, secured, and reported after a breach. Banks, telecoms, ISPs, and critical-infrastructure organizations also face additional security and reporting requirements from the Central Bank, TRA, and national cyber frameworks.

The obligations that typically apply to your organization

Two things follow from this that catch organizations out:

Monitoring has to be running before an incident, not started because of one. Breach notification obligations under Oman's data protection framework assume you already know when something has gone wrong - which is only possible if detection is already in place.

Service providers and technology used for compliance-relevant monitoring should be positioned to meet recognized accreditation and assurance expectations, not assembled from whatever tooling happens to be on hand.

Where Organizations Usually Get Caught Out

In our experience, the gap is rarely the absence of any security tools at all - most organizations already own a firewall and antivirus. The gap is what happens between an alert firing and someone competent actually looking at it: logs that are collected but never reviewed, no defined escalation path when something looks suspicious, retention periods too short to reconstruct what happened, and no documented incident response plan to follow when an alert turns out to be real.

The obligations that typically apply to your organization

Threat detection and response capabilities we deliver

Endpoint Detection and Response (EDR)

Every laptop, server and workstation is monitored for the behavior that precedes a breach - unusual process activity, credential misuse, ransomware-style file encryption - not just known malware signatures. In environments with sensitive data or regulated operations, this shortens the gap between compromise and containment from days to minutes.

Network Threat Monitoring

Traffic across your network is analyzed for lateral movement, unusual data transfers, and communication with known malicious infrastructure. For organizations running multiple sites or a mix of on-premises and cloud infrastructure, this gives one consolidated view instead of gaps between disconnected tools.

Log Correlation and SIEM Monitoring

Security events from firewalls, servers, applications and cloud platforms are pulled into a single view and correlated, so a login anomaly on one system and a data transfer on another are recognized as part of the same incident rather than reviewed in isolation.

Security Operations Integration

Detection and response only works if it's wired into what you already run. We integrate monitoring with your existing firewalls, identity systems, cloud platforms, CCTV and access control where relevant, and IT helpdesk workflows - coordinated in-house because Lyqa Tech also delivers IT Solutions and Services, networking, and physical security, not negotiated between separate vendors after the fact.

Specialized threat coverage

Not every environment is covered by standard endpoint and network monitoring alone:

Cloud workload monitoring for organizations running infrastructure or applications on public or hybrid cloud platforms.

Operational technology (OT) and industrial control system monitoring for manufacturing, logistics and process environments across Sohar and Duqm, where IT-focused tools often miss what matters.

Insider threat monitoring for unusual access patterns from legitimate accounts - often the hardest activity to catch with signature-based tools alone.

Ransomware-specific detection, tuned to catch the early behavioral signs of encryption activity before it spreads across a network.

Email and phishing threat monitoring, since a large share of confirmed incidents still start with a single opened message.

CYBERSECURITY

Managed Detection and Response vs. Tools Alone

A straight comparison to help you decide what level of coverage your organization actually needs.

Feature
Tools Alone (Firewall + Antivirus)
Managed Detection and Response
Alert Review
Left to your internal team, if anyone has time
Reviewed and triaged by analysts before it reaches you
Typical Application
Small, low-risk environments with minimal sensitive data
Regulated, multi-site, or data-sensitive organizations
Coverage Window
Business hours, unless staffed otherwise
24/7 continuous monitoring
Response to Confirmed Threats
Manual, dependent on staff availability
Guided containment as part of the service
Investigation Depth
Limited to what the tool's dashboard shows
Cross-system correlation across endpoints, network and logs
Reporting
Raw logs and dashboards
Management-level summaries plus technical detail for IT
Compliance Support
Minimal, unless separately configured
Retention, escalation and reporting aligned to obligations

Who we work with across Oman

Banking and financial services threat detection

Banking and financial services

continuous monitoring aligned to Central Bank expectations, fraud-adjacent alerting, and incident reporting timelines that hold up under audit.
Retail & facilities operators

Retail and hospitality

payment-data-aware monitoring across multiple outlets, point-of-sale network segmentation checks, and alerting scoped to seasonal traffic spikes.
Government and public sector

monitoring aligned to national cyber governance expectations, sensitive-data handling, and coordination with OCERT-facing reporting requirements.
Logistics & trading

Industrial, logistics and free-zone operations

OT-aware monitoring for Sohar and Duqm sites, coverage that accounts for legacy industrial systems, and detection that doesn't disrupt production networks.
Healthcare organizations

Healthcare

monitoring scoped to patient data systems, segmentation between clinical and administrative networks, and alerting tuned to avoid disrupting critical systems.
How a Lyqa Tech Threat Detection and Response Engagement Runs

Security assessment and baseline

We review your network, endpoints, cloud services and existing tools, and establish what normal activity looks like across your environment before monitoring begins.

Detection architecture design

monitoring scope, data sources, alert thresholds, escalation paths and response authority are agreed and documented before deployment.

Deployment and integration

sensors, agents and log collectors are deployed and connected to existing firewalls, identity systems and cloud platforms with minimal disruption to daily operations.

Testing and validation

detection is validated against simulated threat activity to confirm alerts fire correctly and escalation paths actually work before you rely on them.

Go-live and handover

monitoring goes live, dashboards and reporting are handed over, and your team is briefed on what to expect and how escalation works.

Ongoing management

A managed service that keeps detection rules tuned, coverage current as your infrastructure changes, and reporting up to date for audits and management review.

Request a threat detection and response assessment

Tell us your infrastructure size, industry, and whether you have existing security tools in place, and we will tell you what level of monitoring your organization actually needs before we quote anything.

What Drives the Cost of Threat Detection and Response in Oman

We do not publish fixed prices, because a real number depends on your environment. These are the variables that actually move it:

Monitoring scope - endpoints only, network and endpoints, or full environment including cloud and OT.

Endpoint and user count - driven by how many devices, servers and accounts need to be covered, not company size alone.

Infrastructure mix - on-premises, cloud, or hybrid, and how many locations are involved.

Response depth - monitoring and alerting only, versus monitoring with active containment authority.

Compliance requirements - sector-specific obligations that dictate retention periods, reporting formats and audit support.

Integration scope - how much existing tooling needs to be connected to versus replaced.

Drives the Cost of Threat Detection and Response in Oman

Designing Coverage for Omani Operating Conditions

Compliance-heavy environments

Industrial and free-zone environments

Multi-site and remote connectivity

Local Infrastructure Planning

Why Choose Lyqa Tech Ventures for Threat Detection and Response

Omani-owned, Muscat-based, SME-registered - with the standing that matters in government and enterprise procurement.

Systems integrator, not a box supplier - threat detection is engineered alongside cybersecurity, IT Solutions and Services, and physical security, so monitoring reflects your whole environment, not just one layer of it.

Vendor-agnostic - we specify and integrate what your environment and risk profile require, not what we hold in stock.

One accountable team from assessment to ongoing monitoring, so nobody is between you and a working security operation.

Service areas

Lyqa Tech deliver and support threat detection and response services across Muscat (head office, Bousher), Sohar, Salalah and Duqm, including port, freezone and industrial facilities.

Our Clients

Request a threat detection and response assessment

Tell us your infrastructure size, industry, and whether you have existing security tools in place, and we will tell you what level of monitoring your organization actually needs before we quote anything.

Frequently Asked Questions

What is threat detection and response?

It’s the combination of continuous monitoring and human-led investigation that identifies suspicious activity in your network, endpoints or cloud systems and acts on it – rather than relying on perimeter tools alone to stop everything before it gets in.

Yes. Antivirus and firewalls block known threats at the edge. They don’t investigate an alert, track behavior across multiple systems, or catch an attacker who’s already inside using legitimate credentials – which is where most confirmed incidents actually happen.

Yes. Coverage can be scoped across on-premises networks, cloud platforms, or a hybrid mix depending on where your infrastructure actually sits.

Monitoring, retention and reporting are scoped to your sector’s obligations during the assessment stage, whether that’s banking, government, telecom or general data protection requirements.

Confirmed incidents are escalated to your team with the containment and remediation guidance agreed in your service scope, so you’re acting on a verified issue, not interpreting a raw alert alone.